






Table of Contents
- Key Points
- Defining Model Stealing Attacks
- Motivations Behind Model Stealing Attacks
- Pros and Cons of Mitigation Strategies
- Frequently Asked Questions (FAQ)
- Related Questions



Defining Model Stealing Attacks
What are Model Stealing Attacks?
Model stealing attacks represent a concerning aspect of AI security, aiming to replicate an AI model’s functionality by extensively querying it to extract its decision-making logic
. The ultimate objective is to replicate the model's capabilities without ever gaining access to the original training data or the intricate training processes that shaped its performance. This extraction process hinges on systematically probing the target AI model through numerous input-output pairs.
Attackers carefully craft these queries to glean insights into the model’s responses across diverse scenarios. By analyzing these responses, they aim to approximate the model’s behavior closely enough to create a functional replica. This replica can then be deployed for various purposes, often without the knowledge or authorization of the original model's developers.
The systematic extraction of a model's decision-making process is achieved through input-output pairs, collecting data to approximate the model's behavior .
This kind of malicious replication has different objectives:
- Replication: Attackers aim to create a similar model without access to the original data or training process.
- Intellectual Property Theft: Illegally obtaining proprietary model functionalities, undermining the original developer's competitive advantage and market position.
- Cost Reduction: Avoiding the significant expense of data collection and model training, thereby gaining an unfair economic advantage.
- Competitive Edge: Stealing model capabilities to secure an unfair competitive advantage.
In essence, model stealing attacks are a systematic attempt to reverse engineer the functionality of an AI model, circumventing the time, resources, and expertise invested in its original development.
Motivations Behind Model Stealing Attacks
Understanding the Underlying Drivers
Several motivations drive attackers to engage in model stealing attacks
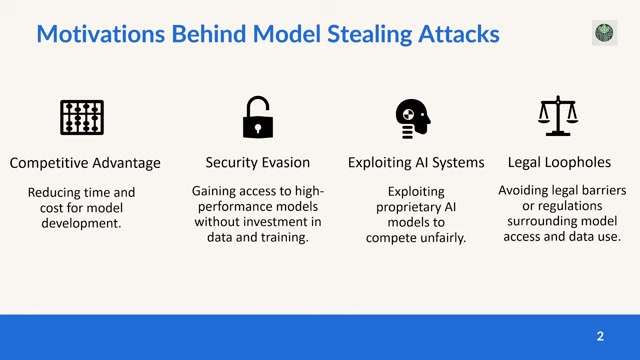
. Understanding these motivations is crucial for developing effective countermeasures. Here are some of the key drivers:
-
Competitive Advantage: Reducing the time and cost for model development is a significant motivator. Attackers seek to bypass the extensive resources required to build high-performing AI models from scratch, gaining a shortcut to market competitiveness.
-
Security Evasion: Gaining access to high-performance models without investment in data and training allows attackers to circumvent security measures and exploit vulnerabilities. They obtain powerful AI capabilities without bearing the associated costs and risks.
-
Exploiting AI Systems: Exploiting proprietary AI models to compete unfairly provides an avenue for attackers to disrupt markets and gain an undue advantage over legitimate providers. This can lead to market imbalances and stifled innovation.
-
Legal Loopholes: Avoiding legal barriers or regulations surrounding model access and data use is another driver. Attackers may seek to exploit loopholes in licensing agreements or data usage limitations, enabling them to use stolen models without legal repercussions.







Most people like






























Report
Please select a reason for reporting
- 13 Reasons to Switch from Snapchat to Text Messaging
- 7 Powerful Speech to Text Apps to Boost Productivity
- 10 Best Speech to Text Tools for Effortless Transcription
- 13 Free Tools to Easily Transcribe Audio to Text
- 15 Surprising Ways Google's Speech-to-Text Boosts Productivity
- 7 Best Free Online Audio to Text Transcription Tools
- 9 Tips to Transcribe Speech to Text Faster and Better
- 13 Best Speech to Text Software for Windows 10 in 2023
- 7 Tips for Choosing the Best Transcriber for Audio to Text
- 11 Reasons Why Dragon Speech-to-Text Apps are Game-Changers
- 6 Secrets to Enhance Your Speech to Text Transcription
- 6 Brilliant Ways to Boost Productivity with Talk-to-Text on Your MacBook
- 6 Ways Transcription Software Converts Audio to Text
- 8 Tips to Transcribe Speech to Text Like a Pro
- 6 Reasons IBM Watson Speech to Text is a Game-Changer
- 14 Powerful Ways Talk-to-Text Improves Your Workflow
- 12 Top Windows Speech-to-Text Software for Efficient Transcription
- 12 Game-Changing Benefits of Apple's Speech to Text Technology
- 9 Powerful Use Cases for AWS Speech to Text Technology
- 10 Easy Steps to Transcribe YouTube Videos to Text
- transcription audio en texte
- online audio transcription
- free audio file transcription
- free ai audio transcription
- audio transcription service
- audio transcription online free
- audio transcription free online
- audio to transcription software
- audio and transcript
- ai audio transcription free
- voice recording to text converter
- translate voice recording to text
- record voice to text
- audio recording to text converter
- voice recording and transcription
- chatgpt voice to text
- gmail voice to text
- speech to text reader
- speech to text ai free
- speech to talk
- How SEO and Marketing Dashboards Empower Agencies to Drive Results
- How to Use AI Tools to Find Internal Linking Opportunities Across a Business Website
- Discover Your Perfect Haircut with AI Hairstyle Apps
- Free Reputation Calculator Tools: How They're Adapting to Score AI Visibility, Not Just Rankings
- Design Professional Flyers for Free on Your Phone
- Best Free Flyer Maker Apps for Android: Design Like a Pro
- How to Know If Your Business Is Ready for an AI Customer Service Agent
- Revolutionizing Storytelling: From Novels to Screenplays with AI
- Create Engaging Animated Explainer Videos with a Free AI Tool
- Stop Multi-Subscribing: Benchmark Top AI Visual Models in One Canvas
- ASOMobile Helps Teams Benchmark App Store Screenshots Against Competitors
- How to Match LMS Software With Your Organization's Training Plan
- Revolutionizing Email Marketing Agency with AI
- How to Convert BTC to HNT
- Unleashing the Power of AI: Cognizant's Roadmap for Transformation
- Frame to Video Review: A Practical Look at Turning Two Still Frames Into Motion
- NVIDIA NIM: Revolutionizing Supply Chain Data Analysis with AI
- Top AI Tools That Help Brands Stand Out Offline (Not Just Online)
- Top 5 Cold Email Software: Maximize Your Outreach in 2025
- Magic School AI: Revolutionizing Quiz & Assessment Generation

Copyright ©2026 toolify